You just booted a fresh Ubuntu VPS and it has a public IP, a root password and nothing else standing between it and the internet's background noise. Here's the hardening pass I run on every box before it does anything useful: SSH locked to keys, netfilter on IPv4 and IPv6, Fail2Ban, automatic security patches and a deploy user that can restart exactly three things.
WeiterlesenPraxisartikel aus dem Engineering-Team von ventx in München: Kubernetes und GitOps, CI/CD mit GitLab, Cloud-Architektur auf AWS, Azure und Google Cloud sowie Security und Observability. Die Artikel sind auf Englisch verfasst.
A minimal three-resource setup for OTLP ingestion on Azure.
Weiterlesen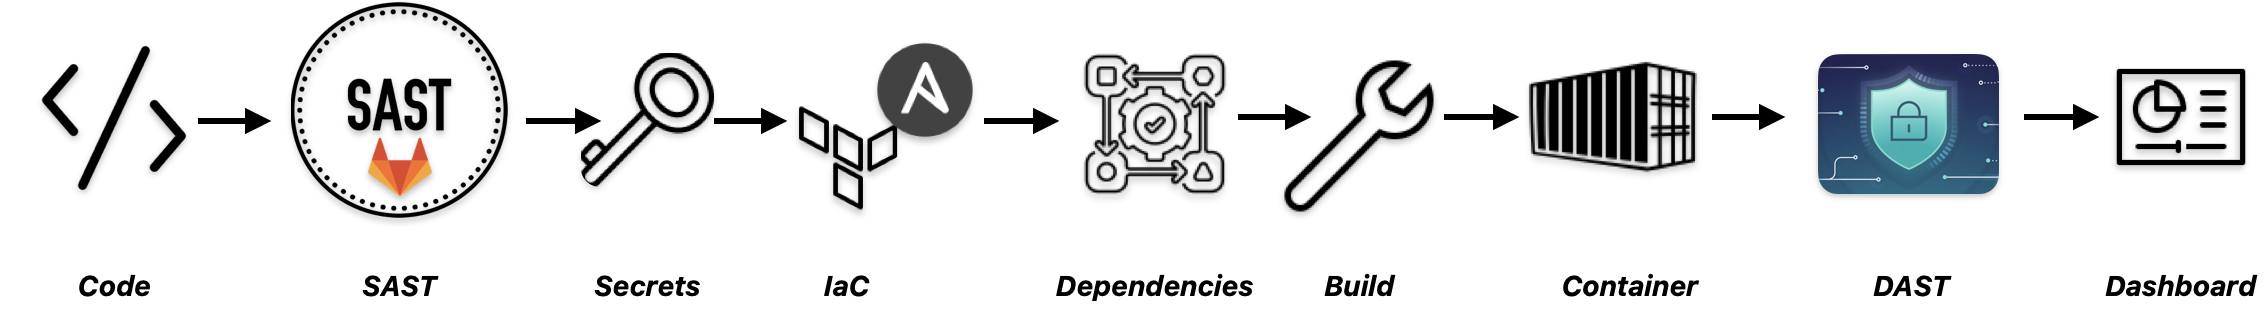
SQL injection in the application code, an RSA private key in version control, 5941 vulnerabilities in the base image. These are not hypothetical risks — they are findings from a real pipeline run. In this post, we show how GitLab Ultimate catches all of them automatically, across seven scanner types, without a single third-party tool.
WeiterlesenA lightweight recipe for hosting Renovate yourself on GitLab CI so you keep control of credentials, schedules, and runner performance.
WeiterlesenThis tutorial guides you through setting up Google OAuth in authentik so that users can authenticate themselves with their Google account.
WeiterlesenMigrating from a traditional Ingress setup to a Gateway API in Kubernetes may sound straightforward at first, but it quickly becomes challenging once multiple services are involved.
WeiterlesenImagine needing to install numerous applications on a Kubernetes cluster. You might automate the process using the Argo CD CLI in a CI/CD pipeline or even resort to manual installation. However, this approach can quickly become overwhelming as you would need to somehow take care of each application installation on its own.
Weiterlesen
To connect an application with Google Cloud resources, we need a Service Account. Service accounts allow you to assign an identity to an application and give that identity specific permissions, such as accessing for example to Google Cloud Translation API but not to Cloud Storage bucket.
Weiterlesen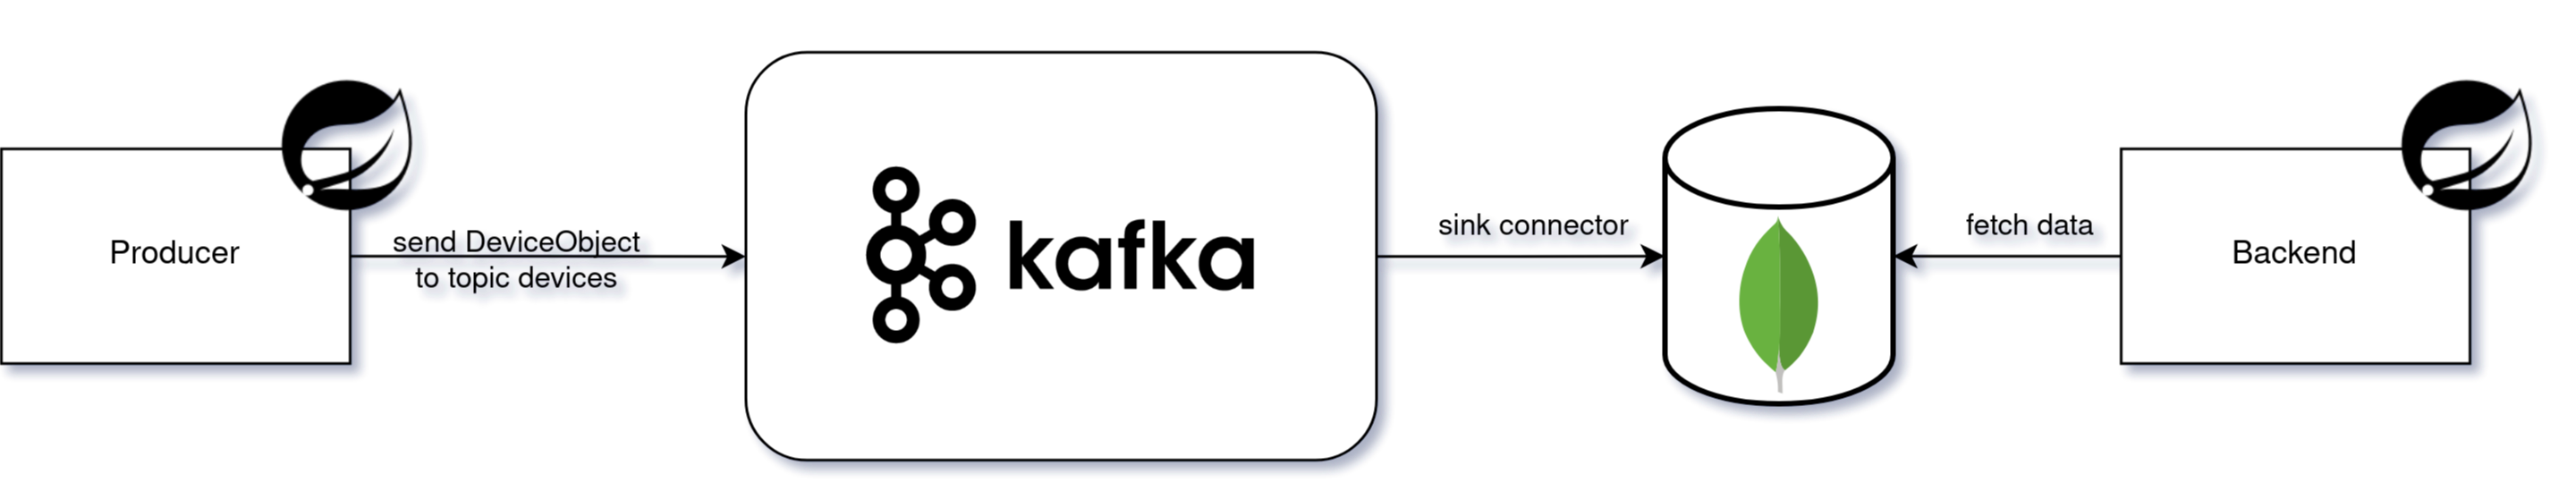
This blog post guides you through setting up a robust data pipeline ideal for handling real-time data streams. We'll use Apache Kafka for data distribution, Spring Boot for our application framework, Avro for efficient data serialization, and MongoDB as our flexible document database. Think of this pipeline as the backbone for applications like IoT sensor monitoring, where data needs to flow seamlessly from generation to analysis.
WeiterlesenIn this blog post I'm happy to guide you through the process of setting up the Flux image update automation feature. In our case it will scan a GitLab container registry for new image versions and automatically updates the manifests (Helm chart releases) in your GitLab repository to always reflect the most up to date image tag.
WeiterlesenIn a previous insightful post by a collegue of mine, titled Connect your Gitlab CI/CD pipeline to AWS via OIDC, the author discussed the basics of connecting GitLab Pipelines with AWS using OpenID Connect. Building upon her valuable insights, this post will
WeiterlesenAt ventx, we like to keep ourselves busy with bite-sized exercises in between projects - this one is about building a serverless Slack app with: Slack Bolt for Python, API Gateway, DynamoDB, Lambda and Terraform
WeiterlesenThis article reflects the current state of technical optimization engineering in cloud infrastructure operations. The Objective is to raise awareness of the topic to cloud engineering individuals. To emphasize, this is not about ML or any similar form of data driven, analytical optimization approaches. The focus here is on continuous configuration space exploring and arranging techniques.
WeiterlesenThe approach to optimize Jenkins builds go hand in hand with test parallelization. Running Parallel tests requires separate Jenkins build containers. The Time consuming issue is how to distribute the build artifacts across the build containers.
WeiterlesenWhen building CI/CD Pipelines to automate the process of deploying resources in AWS via Code (IaC - Infrastructure as Code) you need to give your pipeline runner permission to deploy those resources.
WeiterlesenSecuring the workloads running in your Kubernetes cluster is a crucial task when defining an authorization strategy for your setup. Might say it’s Best Practice**™** to restrict access on a network level and with some sort of authn + authz logic.
WeiterlesenSkaffold is an open source project from Google handling the workflow for building, pushing and deploying your application to Kubernetes. It's client-side only, with no on-cluster component and has a highly optimized tight inner loop, giving you instant feedback while developing.
WeiterlesenConsider the following: You're migrating some microservices to Kubernetes with certain API dependencies, which are not *yet* reachable. There can be plenty of reasons for that: Some dependent services run in a highly secured data center on-prem and are not yet migrated, some APIs may not be fully developed yet.
WeiterlesenA lot of companies are running their entire IT infrastructure still in physical datacenters and while in some scenarios there are a valid reasons to stay on earth, missing knowledge and uncertainties are often a blocker for an informed decision.
WeiterlesenS3 Buckets emit Events which allows you to build serverless and event driven infrastructure. Events in AWS allow us to connect various Services without gluing them together with Code. S3 generated events can be consumed by SQS, SNS und Lambda which provides us great flexibility and a near endless amount of possible infrastructure variations.
Weiterlesen